Know your customer data
KYC records, credit data and transaction history sit across core banking, LOS/LMS, CRM and collections. DPDP.ai discovers and classifies this personal data and maps it by system, owner, purpose and retention.
According to the DPDP Act, a KYC check, credit inquiry, video verification and transaction record is a customer’s personal data. DPDP.ai provides consent, rights requests and vendor oversight into one singular system. This helps in keeping you audit-ready and RBI-regulated.
Under the DPDP Act, banks and NBFCs are Data Fiduciaries, and their BPOs, cloud hosts, bureaus and video-KYC partners are Data Processors. DPDP.ai gives you one platform to meet those duties across every customer channel and vendor.
KYC records, credit data and transaction history sit across core banking, LOS/LMS, CRM and collections. DPDP.ai discovers and classifies this personal data and maps it by system, owner, purpose and retention.
Branch, mobile app, net banking, call centre and digital lending flows each capture consent differently. DPDP.ai offers multilingual, purpose-linked notices and a single consent ledger with withdrawal. Consent signals reach downstream systems in real time.
Consent Manager registration opens on 13 November 2026, and obligations take effect on 13 May 2027. DPDP.ai's phased modules (Consent Core, Flow, Control, Govern) let you start with consent and expand as you go.
Data flow monitoring shows what personal data leaves your environment, who receives it and where it goes. This lets you check each transfer against RBI localisation norms and DPDP transfer provisions.
Vendor risk assessment and processor mapping in the ROPA tie each third party to the data it handles.
Penalties can reach ₹250 crore per violation, depending on the obligation breached. DPDP.ai helps you reduce that risk with evidence-backed controls.
With decades of numerous products, channels and outsourcing. Banks and NBFCs’ customer data has become too scattered. These are the gaps compliance teams encounter first.
Contact SalesCustomer records are stored in core systems, LOS/LMS, CRM, collections and verification tools, so personal data is scattered across many systems.
Branches, mobile apps, net banking, call centres and digital lending flows each follow their own process, which leads to uneven consent and DPDP practices.
Data moves to BPOs, cloud providers, KYC partners and credit bureaus, and every handoff adds risk for the bank or NBFC.
RBI data storage mandates and DPDP transfer rules apply together, so both must be managed side by side.
One customer may hold a savings account, a card and a loan, so a single access or erasure request has to be handled across many systems.
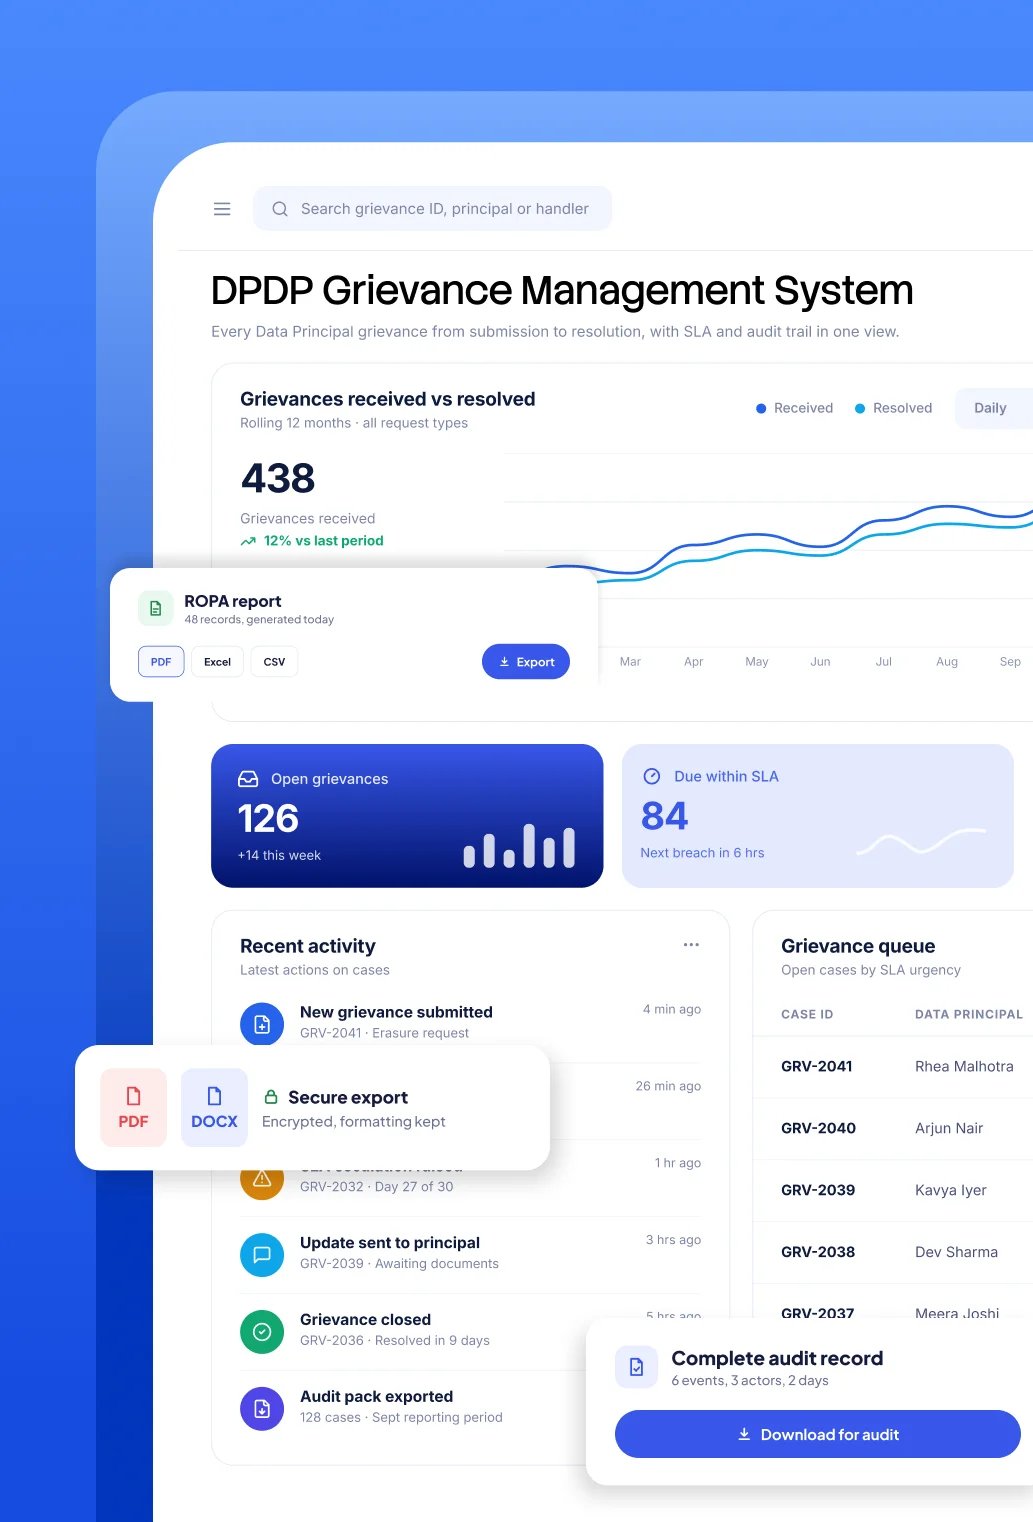
Regulators expect a current view of data flows, consent and processor activity, and a static spreadsheet report no longer meets that bar.
Banking challenge: KYC and biometric data is scattered across main banking, LOS/LMS and vendor systems
How DPDP.ai solves it: Data discovery scans structured and unstructured sources and builds a live map of personal data.
Banking challenge: Consent is collected in different ways across branch, app and net banking
How DPDP.ai solves it: Consent is collected in different ways across branch, app and net banking
Banking challenge: RBI payment-data localisation running alongside DPDP cross-border rules
How DPDP.ai solves it: Each data element is tagged by location, so you see which rule applies to it.
Banking challenge: Heavy reliance on BPOs, collection agencies, cloud and bureaus
How DPDP.ai solves it: Vendor risks are tracked regularly against the terms of their data-processing agreements.
Banking challenge: Rights requests that span several customer systems
How DPDP.ai solves it: Data Principal's requests for access, correction and erasure are routed and closed across connected systems.
Banking challenge: Breach notification within statutory timelines
How DPDP.ai solves it: Collect evidence and prepare an auditable response workflow from detection to notice in time.
Banking challenge: Expected Significant Data Fiduciary duties such as DPIAs and a DPO
How DPDP.ai solves it: Assessments are run on schedule and the evidence trail is stored for review.
Banking challenge: Tracking cookies on net banking and marketing sites without valid consent
How DPDP.ai solves it: Cookie management provides banners and preference storage in line with consent rules.
Questions related to compliance, risk, and technology teams at banks and NBFCs ask us the most.
Talk to an ExpertA bank is considered a Data Fiduciary under the DPDP Act. It is considered one because it processes customer data like KYC records and credit information.
It applies to both existing and new signups. As processing of digital personal data is considered under the DPDP Act, both types of customers are considered.
Yes, they apply together. Organisations must comply with both the DPDP Act and sector-specific RBI directives simultaneously.
A Consent Manager is an entity who is the single point of contact for individuals to give, manage, review, and withdraw their consent with different organisations.
See how DPDP.ai can bring your banking systems, consent and vendors under one compliance view.
By submitting, you agree to our Privacy Policy. We'll only use your details to arrange the demo.